Door categorieën bladeren
Ontdekken
Fiverr Pro
Nederlands
$
USD
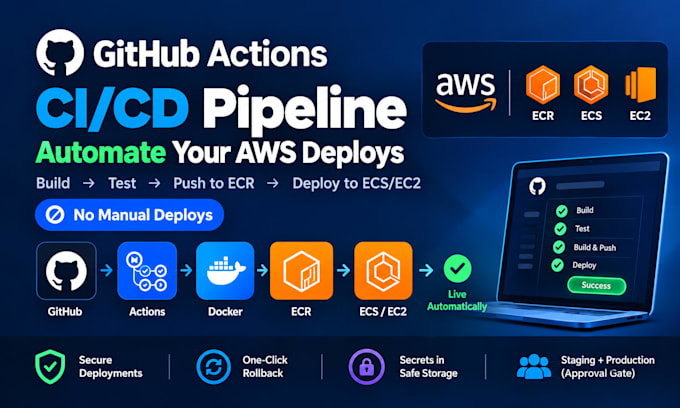
Your releases go out by hand from a laptop, and one bad push can take production down. I set up a GitHub Actions CI/CD pipeline so a merge to main builds, tests and ships on its own, and nobody has to ask one person to push.
It breaks because the release steps live in one persons head. I move them into a workflow that sits next to your code.
You get:
Process: I read your Dockerfile and scripts, build the workflow on a branch, run a real release to staging while you watch, then hand it over.
I need: repository access, an IAM role or user for ECR and ECS, your test and lint commands, and who approves releases.
Message me before ordering so I can confirm your stack and scope.
Tools:
Docker
•
GitLab
•
GitHub
Frameworks:
Npm
Cloudprovider:
Amazon Web Services
•
microsoft azure
Programmeertaal:
Bash
•
JavaScript
•
PHP
•
Python
Expertise:
Installatie
•
Ontwikkeling
•
Configuratie
What access do you need, and is it safe?
Repo access and an IAM role limited to ECR and ECS. The pipeline signs in with that role, so no long-lived AWS keys sit in GitHub. You revoke both when I finish. I never need your root account or your app data.
Do you write my tests?
No. I wire your existing lint and test commands into the pipeline. If you have none, the pipeline still builds and ships, and I leave a clear slot where tests plug in later. Writing tests is outside this gig.
Do you build my AWS infrastructure?
No. Your ECS service or EC2 server, plus staging and production, must already exist. I connect GitHub to them. If the AWS side still needs building, message me and I will quote that separately from this gig.
Which stacks and tools do you cover?
Node.js and Next.js apps that have a Dockerfile, deploying to ECS or EC2 on AWS from GitHub Actions. Jenkins, GitLab CI, Kubernetes and EKS are outside this gig. Message me if your stack differs and I will say so.
How long does it take?
Staging Auto Deploy takes 3 days, Safe Production Release takes 5, Full Team Handover takes 7. The clock starts when I have repo and AWS access, so send both early. Slow access on your side moves the date
What happens if a release goes wrong?
Rollback is one click in GitHub. It redeploys the previous image tag, so you are back on the last working release in minutes. I run it once during handover so you see it work on your own service before I close.
Who can approve production?
You name the GitHub users. Only they can click approve, so a stray merge never reaches production. Some GitHub plans limit this feature on private repos, so I check your plan before I start any of the work.
Can my team release without me afterward?
Yes. Anyone with merge rights ships to staging by merging. Your named approvers release production with one click. The README covers how it works and how to add a new service to the same pipeline later on.
What if I need changes after delivery?
Revisions cover fixes to what I built, so anything that does not behave as described gets corrected. A new service, a new environment or a different cloud is new scope. Add the second service extra or message me.
Why message you before ordering?
So I can read your Dockerfile and confirm ECS or EC2 fits before you pay. It keeps you from buying a tier that does not match your setup, and I tell you up front if your code needs a change first, not after.