Door categorieën bladeren
Ontdekken
Fiverr Pro
Nederlands
$
USD
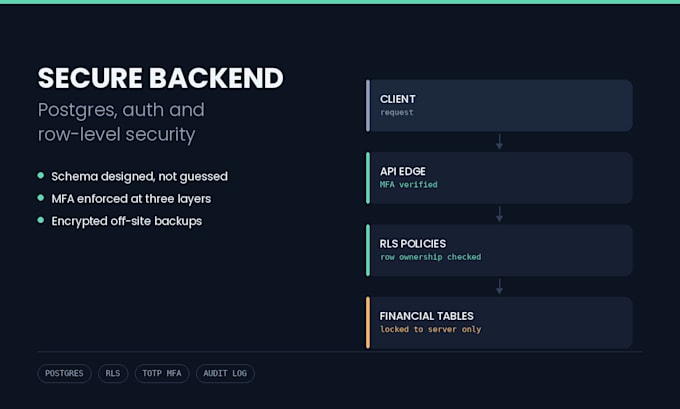
Most Supabase projects I'm asked to look at have the same hole: row-level security is switched on, but the policies let any signed-in user read rows that aren't theirs. It works in testing because everyone is testing with one account.
I build the data layer properly the first time.
What's included:
I built and own the data and security layer of a production B2B platform: Postgres schema, RLS model, multi-factor authentication enforced in the app, in the policies and at the API edge, and financial tables hard-locked against client writes. 3,000+ tests.
Send me your current schema or project and I will tell you what I would change.
Full Stack Developer, Arabic and Hebrew RTL and AI Integration
Talen
