Door categorieën bladeren
Ontdekken
Fiverr Pro
Nederlands
$
USD
Cybersecurity Analyst, SOC, SIEM and API Security Specialist
I help small businesses and SaaS teams understand cybersecurity risks and turn them into practical next steps.
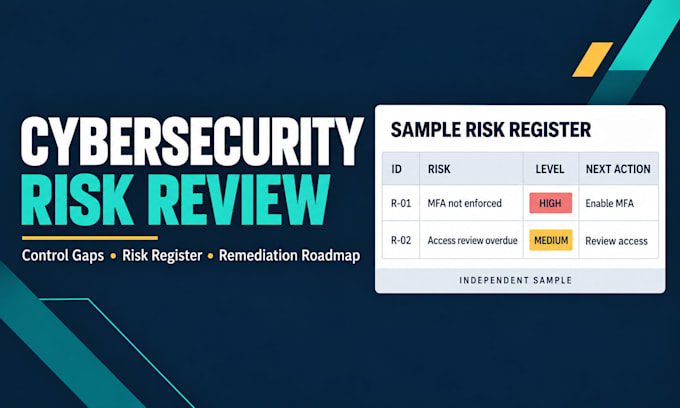
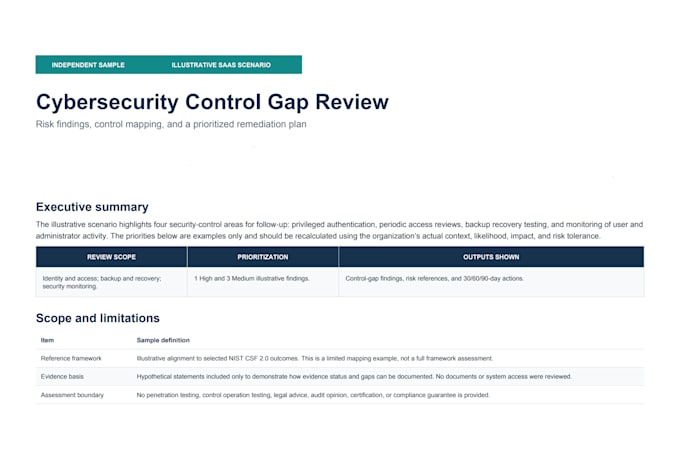
Based on the scope and evidence you provide, I can prepare a focused security risk assessment, identify control gaps, and organize prioritized remediation actions. The review can be mapped to one agreed reference, such as NIST CSF or CIS Controls.
Depending on the package, youll receive a risk register, control-gap summary, and remediation roadmap in clear, client-ready formats.
This service is a technical review based on the information provided. It is not a formal audit, certification, legal opinion, or guarantee of compliance. I do not issue SOC 2 reports or ISO certificates. Please message me before ordering if you need a full compliance program or audit support.


Will this make my company SOC 2 or ISO certified?
No. I provide a scoped technical risk and control-gap review. Certification and formal attestation require the appropriate independent auditor or certification body.
Do you perform penetration testing as part of this gig?
No. This gig is for risk and control review. Ask about my separate API security service for an authorized technical assessment.
What if I don’t know which framework to choose?
Tell me your goal and business type before ordering. I can help define a limited review scope.
Do you need access to my systems?
Usually not. I start with the scope and evidence you provide. Never send credentials through the order.
Can you review a vendor security questionnaire?
Yes, if you select a package with enough scope. Send the questionnaire and relevant evidence before ordering so I can confirm the fit.