Sommige informatie wordt in het Engels weergegeven.
Over mij
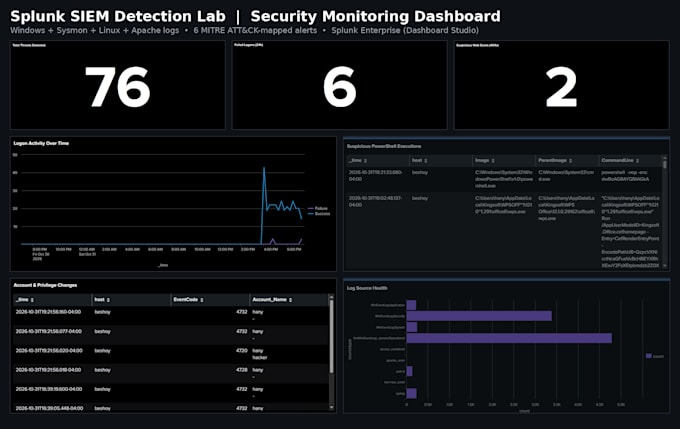
I am a cybersecurity enthusiast focused on SOC operations, SIEM monitoring, and digital forensics. I have hands-on experience through practical labs using Splunk, IBM QRadar, FortiGate, Windows Event Logs, and Sysmon. I can help with Splunk log analysis, SPL searches, SIEM dashboards, security event investigation, and forensic reports. I value clear communication, accurate findings, and professional documentation. I only work with systems and data that clients are authorized to share.... Lees meer