Door categorieën bladeren
Ontdekken
Fiverr Pro
Nederlands
$
USD
Python Automation Engineer and Ethical Hacker
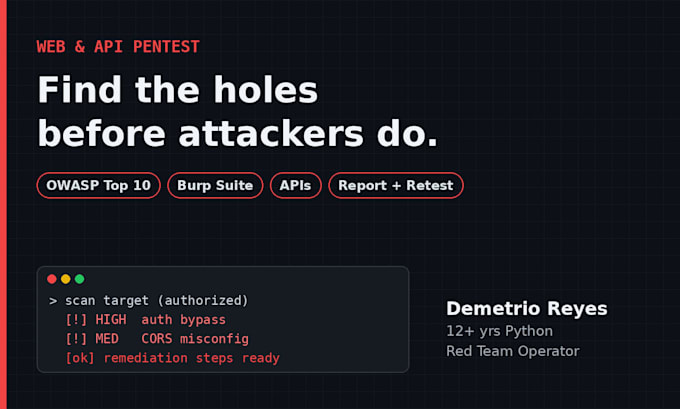
Is your web app or API really secure? I am a Red Team Operator who tests web apps, APIs, SaaS platforms and e-commerce stores for a software factory. I recently found a critical business logic flaw that let users create orders without paying.
I test for: XSS, SQL injection, authentication and authorization bypass, IDOR, file upload flaws, CORS misconfiguration, sensitive data exposure, rate limit bypass and business logic flaws (OWASP Top 10 and OWASP API Top 10).
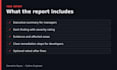
You get a clear report with severity, evidence, steps to reproduce and how to fix each issue. I am also a developer, so I can explain fixes to your team in plain language.
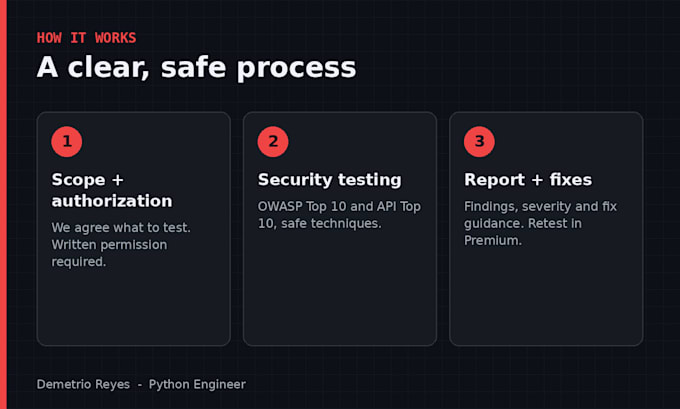
Important: I only test systems you own or are authorized to test. Written authorization and a defined scope are required before starting. Message me first to agree on the scope.
Testapplicatie:
Webapplicatie
Apparaat:
PC
•
Mac
•
Linux
•
iPhone
•
Android telefoon
Will the test break my website or affect my users?
No. I use safe, controlled techniques and avoid destructive tests. If you prefer, I can test a staging environment instead of production.
What do I receive at the end?
A PDF report with every finding, severity (CVSS), evidence, steps to reproduce and clear fixes for your developers. Premium includes a free retest after you fix the issues.
Do you need authorization to test my site?
Yes. I only test systems you own or have permission to test. Before starting, we agree on the scope and you confirm authorization in writing. Your data stays confidential.