Door categorieën bladeren
Ontdekken
Fiverr Pro
Nederlands
$
USD
Your manifests are probably fine. What usually isn't set is the three controls nobody got round to: no default-deny network policy, RBAC wider than it looks, and secrets arriving as plaintext environment variables.
I review Kubernetes manifests and Helm charts for that exact class of gap, then hand you the YAML that closes it.
What I check:
- NetworkPolicy coverage, default-deny, egress rules
- RBAC wildcards, cluster-admin bindings, automounted service account tokens
- Pod security context: privileged, hostPath, hostNetwork, capabilities, runAsNonRoot, readOnlyRootFilesystem
- Resource limits and secret handling
- Image provenance: pinned digests vs floating tags
- Admission control, ingress and TLS
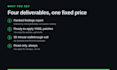
What you get:
- A ranked findings report, ordered by real exploitability, not scanner severity
- Ready-to-apply YAML patches
- A 30 minute call to walk through the findings
I do not need access to your cluster. The manifests are enough. Read-only always: I send you the patches, you apply them.
I have five merged pull requests in Kubescape's Helm charts, including keys their templates read that values.yaml never declared.
Cloudprovider:
Google Cloud Platform
Expertise:
Configuratie
•
Overige
Do you need access to my Kubernetes cluster?
No. In almost every case the manifests, the Helm chart or the rendered YAML are enough. If you want a live read, a temporary read-only kubeconfig for part of the review is fine, but it is never required and I will not ask for write access.
Is this a penetration test?
No. This is a configuration review. I do not attempt to exploit anything, and I do not test your application. If you need a pen test, hire a pen tester. This is the layer underneath that.
What exactly do I receive?
A ranked findings report where each finding says what is wrong, why it matters, and the exact file and line it lives in. Plus the YAML that fixes it, ready to apply. Plus a 30 minute call on Standard and above.
What if you find nothing?
Then you get the report anyway, listing what was reviewed and what was checked, plus any residual risk worth accepting knowingly. No findings is a real result, not a refund conversation, and you keep the documented evidence either way.
Will you change anything in my cluster?
Never. I am read-only by default and I do not apply changes to your infrastructure, your state file or your cloud account. You get the patches and you decide what lands.
Which tools do you actually use?
Checkov and Trivy for the mechanical pass, Gitleaks for secrets, Conftest for policy, Kubescape for Kubernetes posture, and then a manual read of the manifests, which is where the interesting findings come from. Scanner output alone is not a review.
Do you support EKS and AKS, or only GKE?
The manifest layer is the same everywhere, so EKS and AKS are fine for this review. My deepest experience and my certification are GCP, and I will tell you honestly if your question is outside what I can back up.
How is this different from running a scanner myself?
A scanner tells you what the rendered output looks like. It cannot tell you that a security control was never declared, which is the failure I keep finding: the template reads a key, the README documents it, and values.yaml never exposes it.
Can you sign an NDA?
Yes. Send yours, or ask and I will use a standard mutual NDA. I keep your manifests out of any public case study, and I will not name you anywhere without written permission.
Why should I trust a new seller?
Check the work instead of the reviews. Contributions in Kubescape's Helm charts are public and linkable. If the findings report is not worth the money, say so and I will fix it.


