Door categorieën bladeren
Nederlands
$
USD
Koppel je AI aan Fiverr
IT Support and Cybersecurity SOC Analyst
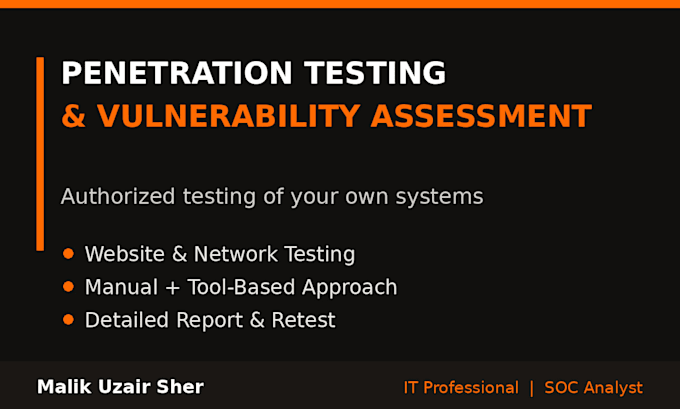
A structured penetration test of your website or network - methodology-driven, clearly reported.
I am a working SOC Analyst (Wazuh SIEM, alert investigation, log analysis) with a BS in Information Technology, now completing an MS in Cybersecurity. I test the way attackers look at your system, then report like a professional: clear findings, real evidence, practical fixes.
Methodology: Reconnaissance, vulnerability scanning, manual verification & safe exploitation of confirmed issues (agreed scope), reporting, retest (Premium).
Scope options: external website/web app, WordPress site, small office network/hosts, API endpoints.
Tools: Nmap, Nuclei, OWASP ZAP, Burp Suite, Metasploit (validation only, agreed scope), Wireshark.
Deliverable: professional PDF report - executive summary, findings ranked by severity with evidence, impact explained in plain English, and prioritised remediation steps.
AUTHORIZATION: Only for systems you OWN or have WRITTEN permission to test. I confirm authorization before any testing begins.
Message me first with your scope for an exact quote - every network is different.
Testapplicatie:
Webapplicatie
Apparaat:
PC
•
Linux
What is the difference between this and a vulnerability scan?
A scan lists possible issues; a pentest manually verifies and safely demonstrates real impact, so you fix what actually matters.
Do you need credentials or source code?
Not required. Test accounts improve coverage for login areas; I will tell you what helps.
Is my data safe?
Testing is non-destructive and agreed in scope beforehand; all findings stay confidential between us.
Can you test a site that is not mine (a competitor)?
No. Only systems you own or have written permission to test.
What do I get at the end?
A professional PDF report your developer or IT team can act on immediately.
