Door categorieën bladeren
Ontdekken
Fiverr Pro
Nederlands
$
USD
Senior DevOps SRE, Full Stack Developer, Blockchain Security
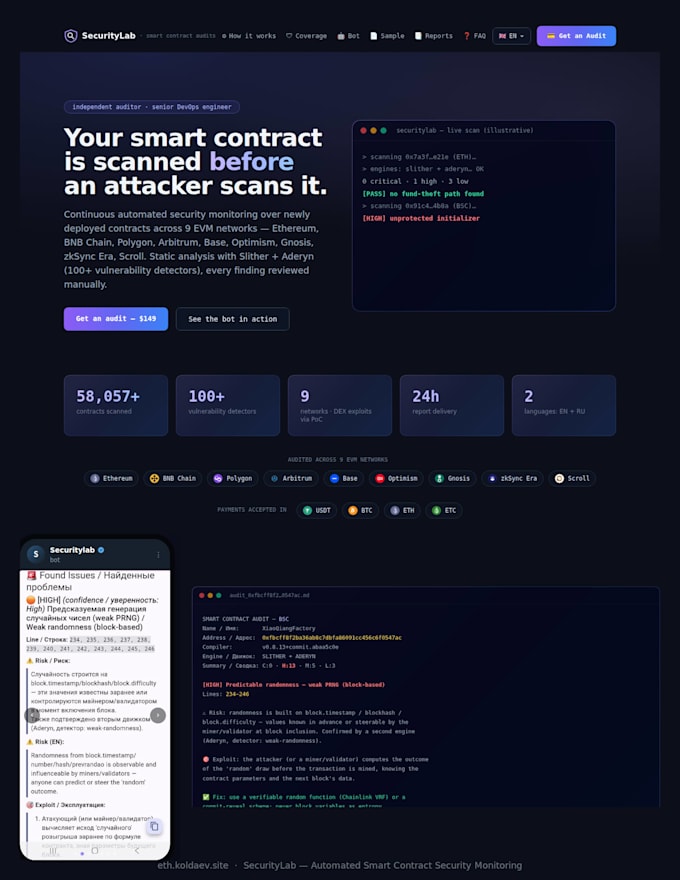
Smart Contract Security Audits: Automated Monitoring + Manual Review across 9 EVM Chains. I run a continuous security pipeline that catches vulnerabilities in Solidity smart contracts before attackers do, combined with a comprehensive manual audit by an engineer. What you get: - Multi-Engine Analysis: Code is analyzed using Slither + Aderyn (100+ combined detectors). No LLM guessing every finding is thoroughly reviewed by hand. - 9 EVM Networks: Full support for Ethereum, BNB Chain, Polygon, Arbitrum, Base, Optimism, Gnosis, zkSync Era, and Scroll. - Mainnet Fork Replay: Where templates exist, exploits are reproduced on a mainnet fork (not theoretical). Cases: BeatXswap oracle manipulation ($63k+ profit reproduced), Yam Finance governance takeover, and Venus Protocol donation exploits. - DEX/AMM Protection: DeFi contracts get an additional custom check for price manipulation risks via pool reads, confirmed by PoC. - Actionable Reports: Detailed risk description, exploit path, and exact code fix (EN/RU). Stats: Over 56,900+ contracts successfully scanned and monitored to date. Secure your protocol. Contact me today!


Token standaard:
ERC-20
Programmeertaal:
Python
Blockchain-platform:
Ethereum
Is this a real audit, or an LLM guessing?
No LLM in the audit pipeline. Every finding comes from Slither and Aderyn — two independent static-analysis engines, the same class of tooling professional audit firms use — cross-checked against each other, with a heuristic fallback when a contract won't compile under either. Where a fork-test temp
What does "PoC-CONFIRMED" actually mean?
t means the exploit was successfully replayed on a forked copy of mainnet at the exact attack block. It reproduces the issue down to the wei. This independent automated and manual validation proves the vulnerability is 100% real and dangerous, not just a theoretical warning.