Door categorieën bladeren
Ontdekken
Fiverr Pro
Nederlands
$
USD
Paying for Microsoft Sentinel and still missing attacks, or drowning in alerts nobody can action?
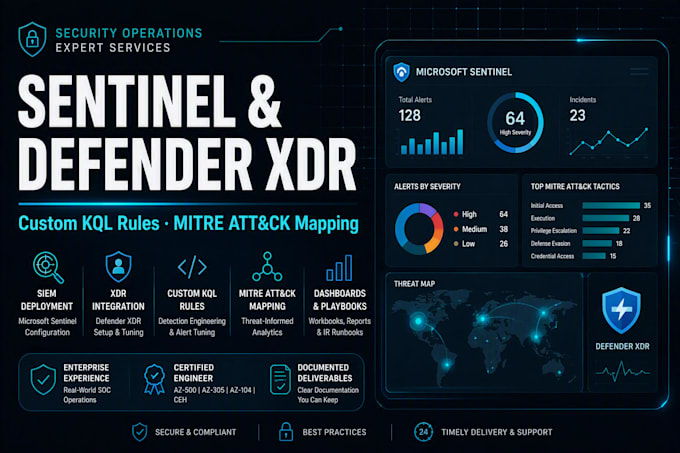
I run enterprise security operations for a large industrial group and build Sentinel and Defender XDR deployments that produce real detections, not noise.
What I deliver:
- Sentinel workspace setup, data connectors and log source onboarding: Microsoft 365, Entra ID, Azure Activity, Event Hub, firewalls, WAF, Linux and Windows servers.
- Custom analytics rules written in KQL and mapped to MITRE ATT&CK - Defender XDR configuration and incident correlation across identity, endpoint, email and cloud apps.
- Alert tuning to cut false positives, with documented suppression logic.
- Workbooks and dashboards for SOC analysts and management reporting.
- Incident response playbooks and a written runbook you keep.
Every order includes a configuration document and a walkthrough call. Message me with your log sources and licence tier and I will confirm scope before you order.
Cloudprovider:
microsoft azure
Expertise:
Installatie
•
Ontwikkeling
•
Configuratie
•
Prestaties
Cloud computing resource:
Overige