Door categorieën bladeren
Ontdekken
Fiverr Pro
Nederlands
$
USD

SOC Lead
Skills
Bekijk mijn diensten

SAFEEYE
Fulltime • 3 yrs 11 mos
SOC Lead
Jan 2026 - Aug 2026 • 7 mos
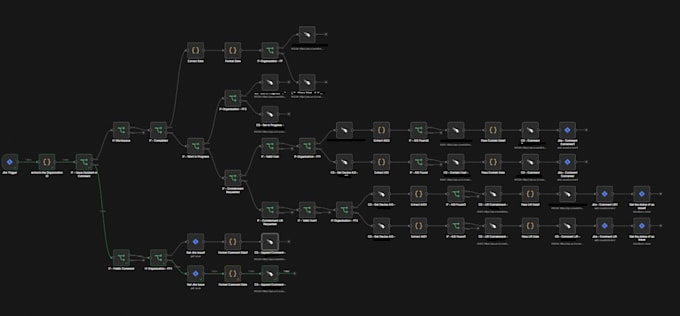
Ticketing & workflow ownership: Led onboarding, implementation, and workflow design of the SOC's Jira Service Management (JSM) ticketing system, including automation for ticket routing and status tracking. • Threat intelligence integration: Onboarded and integrated threat intelligence platforms, enabling operational use across the SOC team. • Detection engineering oversight: Oversaw SIEM rule engineering and detection lifecycle governance, setting tuning strategy, and created/maintained custom decoders and parsers to improve log ingestion accuracy. • SOAR & automation leadership: Led SOAR/automation platform onboarding and playbook development, engineering security workflow automation (n8n) and optimizing incident response processes across the SOC. • Cross-team coordination: Coordinated cross-team SOC operations and owned escalation management for client-facing incidents. • SOC capability & maturity: Drove SOC capability development and detection engineering maturity improvements, including onboarding of self-developed internal tools to raise SOC efficiency. • Reporting & governance: Owned security operations reporting, KPI tracking, and SLA governance across the SOC's client base.
L2 Senior Security Analyst
Jun 2023 - Jan 2026 • 2 yrs 7 mos
SOC automation: Designed and built automated alert-triage and workflow pipelines using CrowdStrike Falcon EDR and n8n, reducing manual documentation effort by ~80% and improving incident response turnaround. • SIEM engineering: Led SIEM implementation, deployment, and EDR fine-tuning across multiple environments, developing custom log parsers that improved ingestion accuracy and reduced false positives. • Incident tracking system: Built a centralized incident tracking system in Microsoft Power Automate integrated with SharePoint, Forms, and Outlook, streamlining incident logging, approvals, and status tracking across SOC operations. • Security policy & SASE: Designed and implemented new security policies within the organization's Secure Access Service Edge (SASE) platform. • Incident handling & VAPT: Led incident handling and Vulnerability Assessment and Penetration Testing (VAPT) engagements, escalating from L1 support to full ownership of client-facing findings and remediation plans. • Client & team leadership: Coordinated a SOC analyst team, ran quarterly client review meetings, and delivered internal training sessions on SIEM tooling and detection workflows.
L1 Security Analyst
Sep 2022 - Jun 2023 • 9 mos
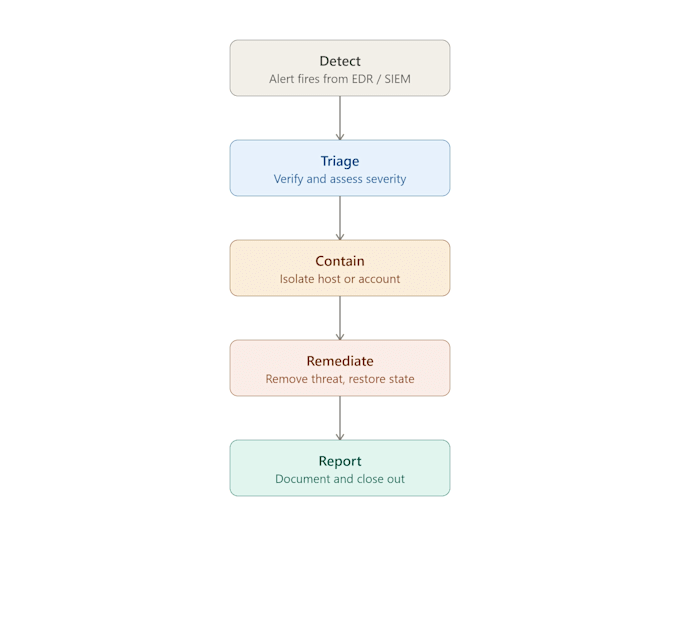
Provided 24/7 SOC monitoring across EDR and SIEM platforms, triaging alerts and escalating true positives within SLA. • Performed incident response — triage, containment support, and reporting — across multiple client environments. • Produced daily and monthly SOC documentation, including threat intelligence summaries and incident reports. • Supported Vulnerability Assessment and Penetration Testing (VAPT) engagements alongside senior analysts.
