Door categorieën bladeren
Nederlands
$
USD
Koppel je AI aan Fiverr
Most websites leak risk through their configuration, not their code. When we checked 1,000 ordinary websites from the outside, 79% had no Content-Security-Policy, 61% had no HSTS and 58% could be framed by any other site. Most of these are one-line fixes.
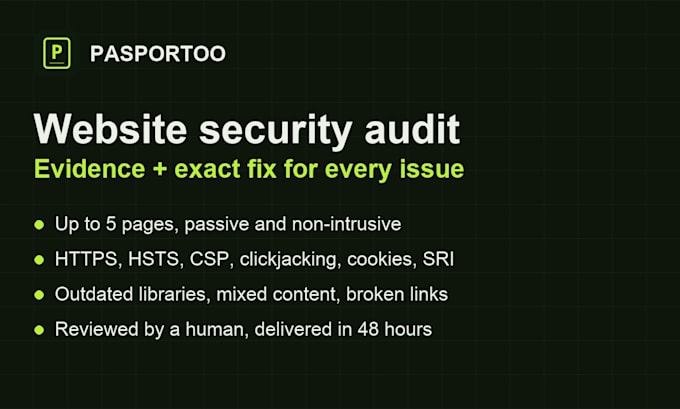
What I check (passive and non-intrusive, no attacks, no login needed):
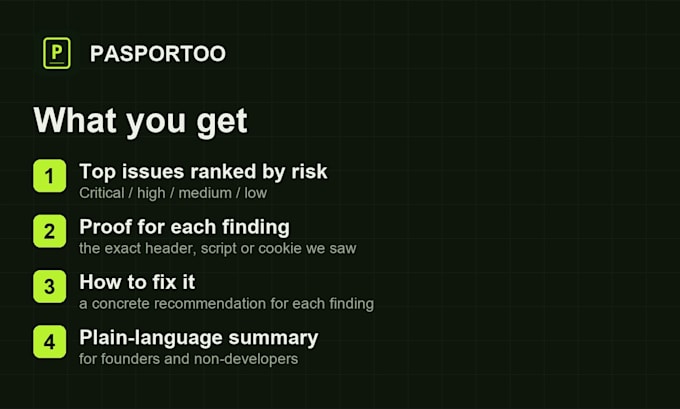
What you get:
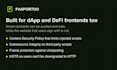
For dApps and DeFi: frontends are a growing target even when the contracts are audited. The Premium package focuses on what limits injected or swapped scripts on the pages where users connect a wallet.
Not included: active penetration testing, login-protected areas, smart contract audits.
Send me your URL and I will get started.
Let erop dat het tegen het beleid van Fiverr voor freelancers is om thema's, templates of andere elementen in het geleverde werk op te nemen die inbreuk maken op de rechten van derden of toepasselijke wetten. Lees er meer over in onze Gids voor verantwoorde digitale creatie.
Website security audits for startups and dApps
Talen
Is this a penetration test?
No. It is a passive review of what any visitor's browser receives. Nothing is attacked or overloaded. For an authorized pentest, message me first.
Do you need access to my server or code?
No. Just the public URL. If you want fixes applied for you, ask about a custom offer.
Will this protect my dApp from a DNS hijack?
Not on its own. DNS and registrar security sit outside the website. The review covers browser-side protections (CSP, SRI, frame protection, HSTS) that limit what an attacker can inject. I point out where DNS and registrar hardening is needed.
Can I get a re-check after fixing?
Yes, in Standard and Premium.