Door categorieën bladeren
Ontdekken
Fiverr Pro
Nederlands
$
USD
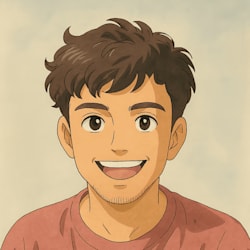


Is your AI-built app leaking user data?
Apps built with Lovable, Bolt or other AI tools often ship with a Supabase database anyone can read, or with keys exposed in the browser. In September 2026, researchers found over 16,000 Supabase databases readable by anyone. I check yours and fix it.
What I check:
You get a plain-English report ranked by risk, plus fixes in the higher packages, retested.
About me: senior software engineer, 5+ years on production payment and subscription systems. Everything is done in writing, no calls. Message me first with your stack and I'll confirm the right package.
I fix apps built with AI tools and n8n automations
Talen
What access do you need?
Read access to your GitHub repo and, for Supabase, a temporary team invite to your project. Never your passwords. You can remove my access when we're done.
Is this a penetration test?
No. It's a code and configuration review of your own app, focused on the mistakes AI builders commonly make. It doesn't come with a compliance certificate. I only test apps you own.
Do we need a call?
No. Everything is done in writing here on Fiverr, and the report explains each issue in plain English.