Door categorieën bladeren
Ontdekken
Fiverr Pro
Nederlands
$
USD
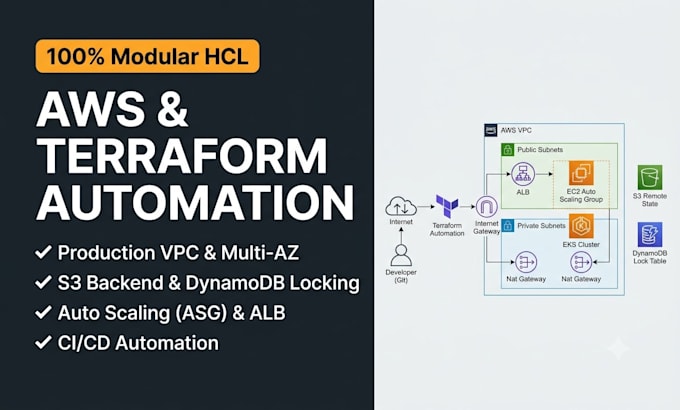
Are you looking to provision secure, scalable, and fully automated cloud infrastructure on AWS? I will design and deploy production-ready environments using Terraform (IaC) tailored to your business needs.
With 6+ years of experience in DevOps and Cloud Engineering, I ensure your infrastructure follows AWS Well-Architect framework standards built for high availability, security, and cost efficiency.
What I Offer:
Why Choose Me?


Tools:
Docker
•
GitLab
•
Jenkins
•
GitHub
•
Hashicorp Vault
Framework:
Terraform
Programmeertaal:
Bash
•
Python
Expertise:
Installatie
•
Migratie
•
Debuggen
What do I need to provide to get started?
You will need to provide your project requirements (or architecture diagram) and access to your AWS account (via an IAM user/role with temporary restricted permissions, or AWS access keys). Do NOT share your root account credentials.
How do you handle sensitive credentials and state files?
I implement strict security practices. Terraform state files are stored securely in an S3 remote backend with DynamoDB state locking and server-side encryption. All credentials and sensitive parameters are managed via environment variables or AWS Secrets Manager / Parameter Store—never hardcoded.
Will I receive modular and well-documented Terraform code?
Yes, absolutely. You will receive clean, production-ready, and fully modular HCL code structured for multiple environments (e.g., dev, stage, prod). Detailed deployment instructions and execution guides (README.md) are always included.
Can you help me integrate the Terraform code into my CI/CD pipeline?
Yes! Depending on the package chosen, I can write automated CI/CD pipelines (using GitHub Actions, GitLab CI, or Jenkins) to automatically run terraform fmt, validate, plan, and apply on push/pull requests.
What if I need changes or support after the order is completed?
All packages include post-delivery revision support to ensure everything works seamlessly in your environment. If you need long-term infrastructure maintenance or future updates, we can set up a custom order or ongoing retainer.