Door categorieën bladeren
Nederlands
$
USD
Koppel je AI aan Fiverr
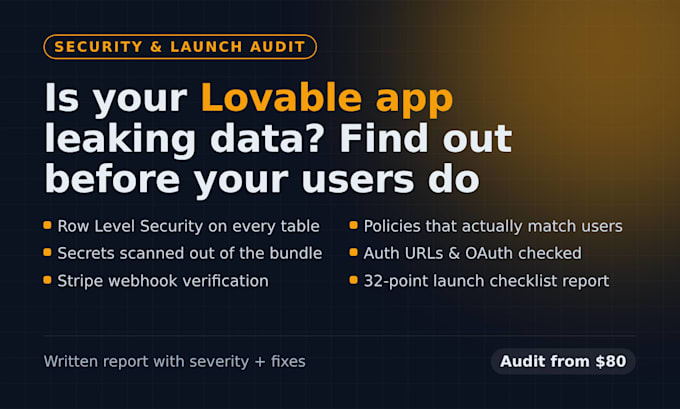
our stack and scope.Built your app with Lovable, Bolt or Replit and about to put real users or real money into it? Most AI-built apps on Supabase ship with security gaps: Row Level Security off or too permissive, auth URLs still pointing at localhost, secret keys in the browser bundle. Users see each other's data, sign-up emails break, or a payment webhook can be faked.
What the audit covers:
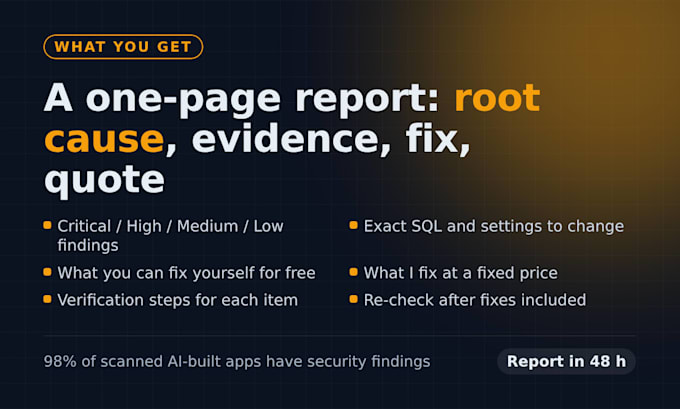
You get a one-page report: each finding with severity, evidence, the exact SQL or setting to change, and what you can safely fix yourself. Standard and Premium include the fixes, applied in a separate branch and verified on your live app.
Access by GitHub invite or project link. No passwords, ever. Message me before ordering.
Telegram Bots and Python Automation Developer
Talen
Do you need my passwords?
No. A read-only GitHub invite or your builder's project link is enough. All secrets stay in your Supabase and Stripe dashboards.
What if you find something critical?
It goes first in the report with the exact fix. In Standard and Premium I apply it; in Basic you can fix it yourself with the SQL I provide, or upgrade.
Which backends and builders?
Lovable (incl. Lovable Cloud), Bolt.new, Replit, Base44, v0 and any React app on Supabase. Firebase or other backends: ask first.
How long is the report?
One page plus an appendix with SQL and settings. Written for founders, not only developers, with severity for each finding.